Add Azure AD B2C auth provider compatibility - #5781
Conversation


✅ Deploy Preview for redwoodjs-docs ready!
To edit notification comments on pull requests, go to your Netlify site settings. |

|
Hi and well done, Leon! 👏
@dac09 @dthyresson Once above is addressed, can we bring it the PR to main for a canary build? I could update the Auth Playground, unless we want to keep it canary free, and a production app. |


|
Hey @jeliasson
|
|
LGTM. |

|
Thanks @Leon-Sam for this! I looked at your auth playground PR and see that you have it working. We can help in that PR to define some enviers, etc. Could you resolve the conflicts and I have sorted the PR to run CI now. Again, many thanks. |
…ation of B2C docs
|
Just fixed the merge conflicts from main due the Auth documentation change. Let me know if I need any other tweaks. |


|
I just tried
|
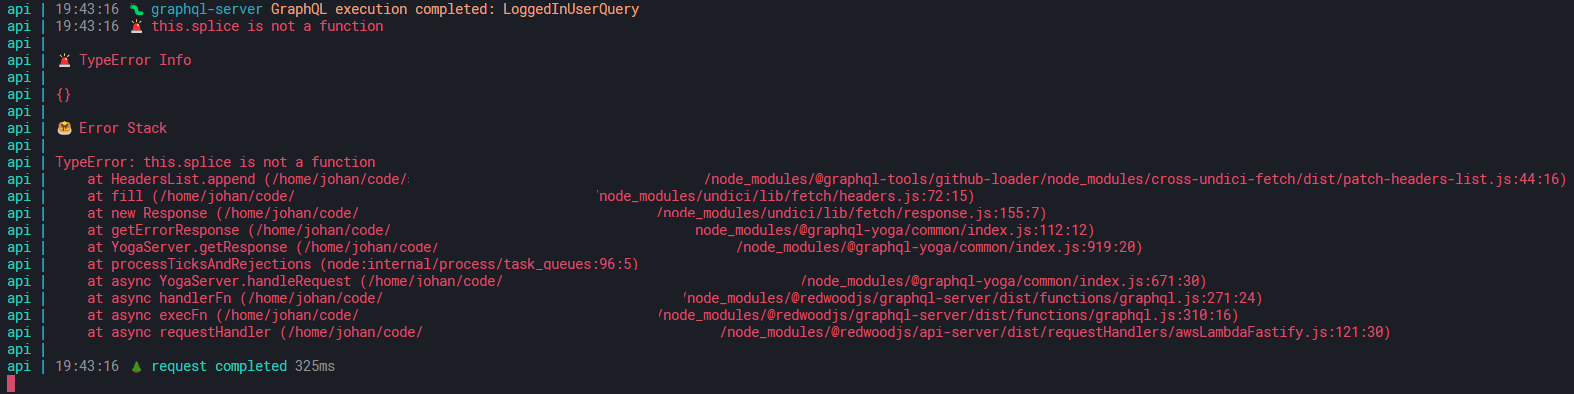

@jeliasson I think this is unrelated, you node_modules probably just needs a clean and reinstall - haven't seen that one in a while! This was an issue in cross-undici-fetch that was resolved a while ago. |
|
@dac09 Yeah me too. I just catched David during the RW Office Hours to let him know about it. I did the classic delete/install, but that did not do the trick this time. Currently pushing it to the dev enviorment to see if it yields the same issue here, otherwise borked local env. |
Right @jeliasson and I just spoke and I knew I recognized that "splice" message from awhile back. See: #5526
|

|
Lockfile was the baddie. Thanks. I'll try out new canary a bit later. |
|
From what I can see, canary Thanks @Leon-Sam @dthyresson @dac09 |

…ctmode-gen

* 'main' of github.com:redwoodjs/redwood:
  validateUniquess optional prismaClient parameter (redwoodjs#5763)
  fix(deps): update dependency prettier to v2.7.1 (redwoodjs#5808)
  fix(deps): update dependency eslint to v8.18.0 (redwoodjs#5806)
  fix(deps): update dependency systeminformation to v5.11.21 (redwoodjs#5805)
  fix(deps): update dependency @apollo/client to v3.6.9 (redwoodjs#5804)
  chore(deps): update dependency firebase to v9.8.3 (redwoodjs#5799)
  Add Azure AD B2C auth provider compatibility (redwoodjs#5781)
  chore(deps): update dependency esbuild to v0.14.47 (redwoodjs#5798)
  Maps JSON GraphQL Scalars to Prisma Json field types for compatibility (redwoodjs#5796)
  fix(deps): update prisma monorepo to v3.15.2 (redwoodjs#5789)
  fix(deps): update dependency core-js to v3.23.2 (redwoodjs#5790)
  fix(deps): update dependency webpack to v5.73.0 (redwoodjs#5755)
  docs: update disable api layer/database to include disabling prisma (redwoodjs#5528)
  Fix typo in testing docs (redwoodjs#5782)
  fix typo (redwoodjs#5777)
  docs: Replacing Prisma.xxx types with types from 'types/graphql' (redwoodjs#5740)
  Reorganize auth docs into sub-categories (redwoodjs#5787)
…b-issue-forms

* 'main' of github.com:redwoodjs/redwood: (40 commits)
  Update link to auth/providers implementations (#5826)
  fix(deps): update dependency qs to v6.11.0 (#5836)
  Docs -> Tutorial - Update comment-form.md - Minor Typo (#5837)
  fix: have user config for `addons` and `stories` take precedence (#5780)
  chore(deps): update dependency @tsconfig/docusaurus to v1.0.6 (#5834)
  chore(deps): update dependency @auth0/auth0-spa-js to v1.22.1 (#5831)
  Fix misnamed forbidden page route (#5832)
  fix(deps): update dependency concurrently to v7.2.2 (#5830)
  Router tests: More advanced auth mock (#5742)
  fix(deps): update dependency react-hook-form to v7.33.0 (#5809)
  fix(deps): update dependency qs to v6.10.5 (#5829)
  fix some grammar issues (#5778)
  fix(deps): update dependency ci-info to v3.3.2 (#5828)
  validateUniquess optional prismaClient parameter (#5763)
  fix(deps): update dependency prettier to v2.7.1 (#5808)
  fix(deps): update dependency eslint to v8.18.0 (#5806)
  fix(deps): update dependency systeminformation to v5.11.21 (#5805)
  fix(deps): update dependency @apollo/client to v3.6.9 (#5804)
  chore(deps): update dependency firebase to v9.8.3 (#5799)
  Add Azure AD B2C auth provider compatibility (#5781)
  ...

5 participants


Changes:
🚀 Azure AD B2C authentication is now supported
📖 The Azure AD authentication section of the documentation has been amended to provide tips for Azure AD B2C setup
🐛 Fixed a bug in the current form of Redwood's Azure AD auth would cause the MSAL library to lock up with a "interaction_in_progress" error
Logic behind code changes:
The existing Azure AD auth provider implementation almost worked perfectly with the Azure B2C product. 2 small changes had to be made.
1. Added an additional environmental variable for JWT issuer check
I made some small tweaks to the existing Microsoft AD Auth provider to allow for compatibility with Microsoft's Azure AD B2C product. It required some small tweaks to allow for alternative strings to be used during the JWT verification process (Specific Azure AD B2C thing). The changes should be fully backwards compatible with previous Azure AD installs.
2. Removed logic to search browser url for "#code="
Previously when the AuthClient found a "#code=" in the url on mount, then it would trigger the MSAL to handle the redirect. This was brittle for 2 reasons.
Testing Method:
I made a throwaway app on my end with Azure AD B2C credentials/user flows.
The test app can:
Request:
@jeliasson Could you make sure that this PR doesn't break any Azure AD integrations you already have?