Repository navigation
Recovery launcher: land #142 - #154
Conversation


…y launcher Conflicts: Info.plist keeps both keys; main.swift answers --backstop first, then resume-frozen and the session command; releasing.md keeps both sides' checks. # Conflicts: # Resources/Info.plist # Sources/Insomnia/main.swift # docs/releasing.md

Codex Review Summary: ✅ CompletedThis comment shows the latest Codex review activity on this pull request.
ℹ️ About Codex in GitHubYour team has set up Codex to review pull requests in this repo. Reviews are triggered when you
Codex reacts with 👀 while any review is running, comments if it has suggestions, and reacts with 👍 once all reviews finish with no findings. |

Since the native --backstop command landed, runAgent only ran that command, so no test executed LaunchdBackstop.agentProgram any more. The plist still uses that shell verifier for an older bundle, a requirement without cdhashes and SIP that is not known to be enabled, and install.sh writes the same fallback. Its remaining tests only read the program text or the plist. The intact, edited-script and wrong-build cases now live in one helper that runs twice: once with the native command, as before, and once with the ProgramArguments plistDictionary writes for a target without a native executable, run with HOME in the scratch tree. The shell run checks the exit status, whether the sealed script ran, and the one-line refusal in ~/Library/Logs/Insomnia/insomnia.log with codesign's reason, as main's test did. The native assertions are unchanged. Checked by breaking agentProgram three ways and running the shell test: dropping the -R requirement fails it 4 times (the wrong build runs the script, exits 0 and logs nothing), exiting 0 on refusal fails it 2 times, and skipping verification fails it 3 times. The native test passed with the requirement dropped. swift build and swift test --filter PackagingTests pass, 29 tests, 0 failures.

|
The full suite at |
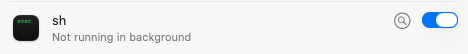
A run in a macOS 27.0.1 VM with SIP disabled installed the external shell verifier, as designed, and Login Items listed the recovery agent as sh with a generic icon. Only the native plist carries AssociatedBundleIdentifiers, so the Insomnia name and icon come with SIP enabled. install.md and the release check now say so, so a tester on a Mac with SIP off doesn't read the sh row as a failed upgrade.
VM evidence at 38b0ef6: the recovery agent with SIP disabledA macOS 27.0.1 VM with System Integrity Protection disabled, the head's ad-hoc build (CDHash
Login Items & Extensions, before the upgrade, after it and after the restart, showed the same row each time:
That is the shell verifier as designed: only the native plist carries Not covered. The native path needs SIP enabled, which a VM here doesn't have: Login Items showing Insomnia, |
 krishhgg
added
the
accepted
|
@codex review |
|
Codex Review: Didn't find any major issues. Can't wait for the next one! Reviewed commit: ℹ️ About Codex in GitHubYour team has set up Codex to review pull requests in this repo. Reviews are triggered when you
If Codex has suggestions, it will comment; otherwise it will react with 👍. Codex can also answer questions or update the PR. Try commenting "@codex address that feedback". |
🛡️ Codex Security Review · Automatically triggeredSecurity review completed. No security issues were found in this pull request. Reviewed commit: Only the user who started this review can view the report in Codex. ℹ️ About Codex security reviews in GitHubThis is an experimental Codex feature. Security reviews are triggered when:
Once complete, Codex will leave suggestions, or a comment if no findings are found. |
|
Real-Mac run at 89a5f33 on the maintainer's MacBook (Mac17,2, macOS 26.2, SIP enabled), installed with that build's cdhash pinned. Everything passed. Login Items. macOS's own Login Items record (
The launcher's pinning.
Recovery after a log in. The agent loaded at login ran every minute, 11 runs in the first 11 minutes, all exiting 0. A 5-minute session then disabled sleep and turned on Low Power Mode, and the app was force-quit. 34 s after the session's end time, the agent restored both and cleared the journal: The app also opened at login. That came from its own Open at Login entry, which was there before the install, not from the agent. |


Login Items now shows Insomnia, not an unnamed shell script. The recovery agent that undoes an abandoned session runs a small native launcher inside the app, pinned by its code signature, which checks the bundle and then runs the sealed backstop script.
This lands #142 by @ilya-the-frog at bf8a75a. The commit is merged here unchanged, so GitHub marks #142 merged when this one merges and its author keeps the credit. #142 conflicts with #146 (the session command line), which lands first, so it can't merge as it is.
To @ilya-the-frog: please don't push to your branch now. A new commit on it isn't in this pull request, so #142 would stay open instead of showing as merged.
The base is
integration/wave1-base: main with #146 and #147 (which carry #145) merged, as main will be once they land. When #147 merges, this pull request's base changes to main and nothing else changes.Conflicts resolved
Maintainer commits
38b0ef6: the packaging tests run the intact, edited-script and wrong-build cases through the shell verifier as well as the native command. The plist still falls back to the shell verifier for an older bundle, a requirement without cdhashes and SIP that is not known to be enabled, and install.sh writes the same fallback, but since Show Insomnia in Login Items with a pinned native recovery launcher #142 no test ran it. Breaking the verifier three ways (no requirement check, exit 0 on refusal, no verification) fails the new run.Tests
The full suite at this head,
38b0ef6: 1408 tests, 0 failures, on macOS 26.2 on the maintainer's MacBook. Hosted CI runs on macOS 26 and 27.Review
The merge is clean at 0981a6a, the same tree as
f0f183e; only commit messages changed. That review checked the command order in main.swift, that an install, an interrupted install or an uninstall cannot leave the recovery agent running something unpinned, and that the release checklist still covers Login Items, the launcher's spawn constraint and recovery after a restart.38b0ef6had its own review with no findings: the shell run executes the exactProgramArgumentsthe plist writes, and it checks what main's test checked before #142.Evidence
To run on the owner's MacBook at the final head: install, Login Items shows Insomnia, the recovery agent's launcher carries the expected spawn constraint, and after one restart the agent runs and recovers a session journal.


The PR appears safe to merge; no new actionable issue was found.Summary
The recovery agent can now start
Insomnia --backstop, letting Login Items identify the app instead of a shell.--backstopcommand checks the bundle before recovery.The earlier unnumbered shell-coverage finding is addressed. Following krishhgg’s fix, the shared cases check intact bundles, edited scripts and wrong builds through both launchers. No new actionable issue was found. macOS tests and hardware checks were not run in this review.
Diagram
%%{init: {'theme': 'neutral'}}%% flowchart TD A[Choose recovery launcher] --> B{Native command, cdhashes and SIP enabled?} B -->|Yes| C[launchd checks executable hash] C --> D[Insomnia --backstop checks bundle] B -->|No| E[Shell verifier checks bundle] D --> F{Bundle passes?} E --> F F -->|Yes| G[Execute sealed backstop.sh] F -->|No| H[Log refusal and exit]Reviews (4) · Last reviewed commit: "Merge main into recovery-launcher" · Reviewed by Greptile