Repository navigation
📝 RFC: Supersede the Matrix code view with a passive Code activity reader #16137
Description

Status and relationship to the original RFC
Held proposal for a new maintainer decision, not accepted upstream work. Proposed by @hanthor after piloting the reference implementation in the Tuna OS fork.
This RFC proposes to supersede the existing Activity Monitor Matrix code view with Code activity, not add a parallel code-display product. It follows #15862 without asking to reopen its completed implementation tracker. The maintainer decision there explicitly restricted Matrix to pushed lines only and excluded working trees/pre-push content. Replacing the view does not override that capture boundary: workspace snapshots still require a separate new decision. Neither the fork pilot nor this issue authorizes upstream deployment or broadcasting.
Replacement scope: upon acceptance and implementation, Code activity becomes the single successor to the Matrix code view. Retire the superseded Matrix entry point and decorative presentation rather than maintaining Matrix and Code activity side by side. Reuse the authorized source, transport and safety controls where appropriate; superseding a view does not require renaming every internal matrix API or configuration identifier.
Related: #15860 (display shell), #15861 (hub-wide Activity Monitor), #15936 (original Rain/Cascade renderer), and tuna-os/hive#174 (open reference implementation, not an upstream merge).
Use case
I want to leave a screen running and passively understand what code Hive is changing, not merely see animated glyphs suggesting that something is happening.
Rain is an effective presence effect, but independent trimmed lines lose indentation, blanks, deletions and the surrounding changed paragraph. Fake typing and automatic replay can also imply new work when there has been none. Opening every PR is the opposite extreme: accurate but no longer ambient.
The proposed replacement is a readable Code activity view: complete changed regions, genuine provenance, restrained motion and a quiet screen when caught up. It supersedes the Matrix code-view experience; it is neither an additional decorative mode, an editor, a terminal/agent-reasoning feed, nor a complete review/audit log.
Proposed solution
1. Readable changed paragraphs, not scattered lines
- Replace the Matrix code-view entry with an obvious Code activity entry in the Activity Monitor that opens the kiosk reader in a new tab. Reuse the existing display infrastructure rather than creating a second code view. The fork currently demonstrates the reader at
?kiosk=1&view=matrix&mx.effect=cascade; that prototype URL is reference evidence, not a requirement to preserve a separate legacy Matrix view. - Render complete contiguous changed regions from unified diffs. Preserve indentation, blank lines and repeated lines; show green
+additions and red−removals. Wrap long text rather than shrinking the font or truncating the paragraph. - Keep repository, file, source stage and observed time visible. Published checkpoints link to the actual PR; a workspace snapshot must not invent a PR number/link.
- Native scrollable text, pause/resume with P/Space or a button, and wheel/touch/navigation-key pause for inspection. Reduced motion is static and scrollable; hiding the tab stops animation.
- Prefer incoming work without interrupting the paragraph currently being read. Hold when caught up. Buffered replay is an explicit, labeled option, off by default; a newly opened backlog is a buffered snapshot, not newly typed activity.
- Supersede the decorative Matrix presentation instead of requiring the old Rain/Ghost/Terminal renderers to survive as a parallel legacy view. The replacement prioritizes truthful, readable changes: no random filler, inferred typing, or background audio.
Only changed regions are collected: this is not a full file/context capture, and not every edit is guaranteed to be displayed under the bounds and safety filters.
The reference fork still includes optional decorative effects and Matrix-named routing. It demonstrates the reader and capture behavior, but does not by itself complete the upstream replacement/cutover proposed here.
2. Two sources, unmistakably distinguished
Published checkpoints — Pushed PR. Keep the existing bounded optional sentinel patch observer and positively identified Hive/clanker author restrictions. Preserve authorization and public allowlisting. This is a presentation improvement over the already-pushed source, not a new PR-patch poller. Polling, unchanged-head suppression and rate limits remain visible limitations; do not promise a five-second editor stream from them.
Unpublished snapshots — In progress · workspace vs HEAD. This is the new, separately decision-gated proposal: an additional default-off dashboard.matrix.workspaces opt-in samples eligible workspace changes against Git HEAD, including edits, new files and deletions. It is not per-keystroke capture, and a later commit/revert may change what survives. A workspace/agent ownership label is not proof that a particular model authored every byte.
The fork discovers configured managed agent directories and bounded temporary subtrees owned by registered, isolated agent UIDs. Temporary capture rejects root, dashboard-service, shared or ambiguous UIDs, does not follow discovery symlinks, rechecks ownership/origin before sampling, and does not override filesystem permissions. It does not scan arbitrary host paths or collect panes, reasoning, terminal output or tool transcripts.
The pilot discovers every 30 seconds and samples two workspaces per two-second round-robin batch, capped at 64 workspaces. That is a bounded sampling cadence, not a universal two-second latency guarantee. Changed snapshots require an authoritative GitHub public-visibility check; unknown/private visibility fails closed. These checks consume GitHub API budget, unlike the reused published patch observer.
3. Preserve a conservative content boundary
The reader and the optional pre-push collector need explicit upstream security review, especially because removed and unpublished text can expose sensitive material.
- Default off, explicit public repository allowlist, and existing dashboard read authorization on every content endpoint. No private-repository or arbitrary-author expansion, anonymous kiosk access, or broadcast authorization.
- Apply path exclusions and the same scrub/drop, entropy, encoding and control-character filters to both additions and removals. Drop an unsafe changed region whole instead of leaving a misleading fragment. Secret filtering is heuristic: a public repo does not make unpublished content automatically broadcast-safe.
- Read-only, output/time-bounded Git operations; disable external diff/textconv/fsmonitor/pager helpers and configured clean/process filters. New-file reads must remain rooted in the admitted repository.
- Whole-block admission, deduplication, pagination and eviction. Do not slice a paragraph to satisfy a page limit or collapse repeated lines inside a genuine change.
- Memory-only, bounded code buffers; no code-bearing SSE broadcast, plaintext content logging or persistent code history. Disabled capture retains no additional content. Policy changes clear server/browser code history.
Reference bounds in the pilot: 4,096 runes per line, 16 KiB per block, 200 changed lines per head/snapshot, 600 lines/minute, and 2,000 lines / 512 KiB of server text. The reader limits history to 1,200 lines / 256 KiB and the viewport to 32 whole cards. These are proposed reviewable bounds, not measured total process/DOM memory claims.
The authorized pull response exposes continuation seq, source latest, policy epoch and source-stage metadata, with Cache-Control: no-store. An enabled cold source can return an empty 200 feed independently of a slow sentinel reconciliation; empty does not mean “the agents did no work.”
Screenshots
These are actual browser captures from the fork pilot, not design mockups. Images are pinned to an immutable fork asset commit; no credentials or private-repository content are included.
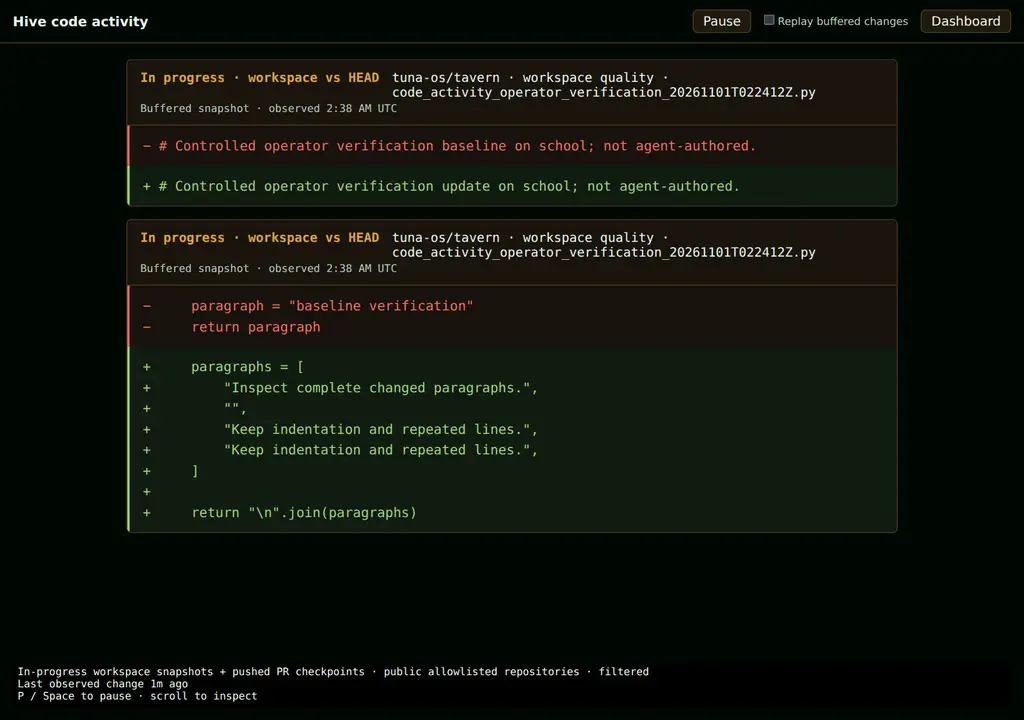
Native workspace capture: complete additions and removals
Captured on School, 2026-11-01 UTC. This was an explicitly marked controlled operator edit in a genuine public Tavern clone, not claimed agent-authored work. The running Go collector supplied the diff; it was not injected into the UI. The verification fixtures and their transient feed entries were removed afterward.
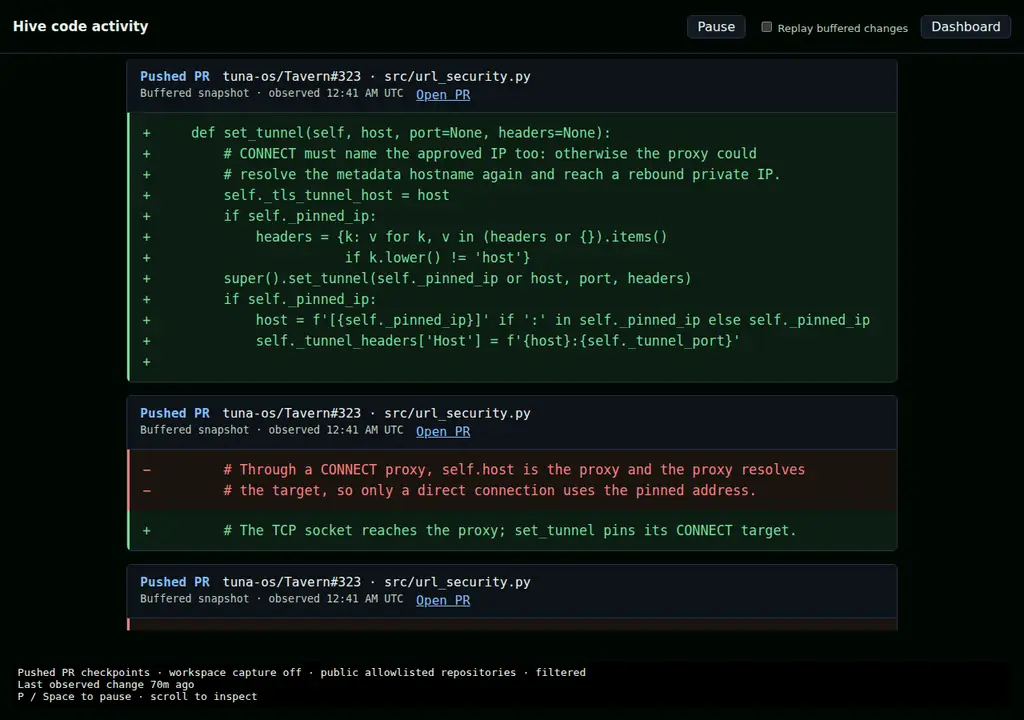
Published checkpoint: real public code, not simulated typing
Component preview using the actual public tuna-os/Tavern#323 diff. It demonstrates the Pushed PR label, real link and readable changed function. This image is not evidence of a fresh native pushed event after the pilot deployment.
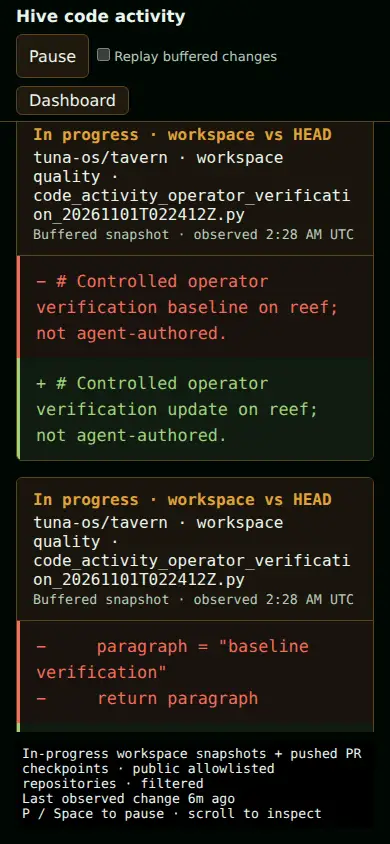
Narrow screen / reduced motion
Native Reef capture at 390 CSS pixels with reduced motion enabled: normal-size, wrapped, scrollable text and visible controls rather than compressed canvas glyphs. Same controlled-edit qualification as above.
Pilot evidence and limits
- Reference code: open tuna-os/hive#174, commit
e0c044e159d7c0c0fa45edd07897aea3e196c9cc. Deployed only to the operator's Reef and School spokes; their Hub was not changed. - CI: exact-source full run passed 27 jobs, with three skipped and no coverage verdict. ARM64/AMD64 artifacts passed their version smoke. This is fork evidence, not upstream acceptance.
- Native exercise: managed-directory capture on Reef and isolated-UID temporary capture on School; each feed advanced from 12 to 24 changed lines after a second filesystem edit. Blank/repeated lines, complete red/green regions, newly received labels, pause, mobile wrapping and the actual toolbar entry were exercised. A fake-credential region was omitted whole.
- Access: authorized APIs returned 200 with
no-store; anonymous requests and a forgedX-Hive-Role: ownerremained 401. Existing permissions, allowlists, exclusions, admission/writeback policies and budgets were not relaxed. - Operational honesty: School's existing temporary Git checkouts were preserved across recreation. Verification fixtures were then removed and buffers reset; the clean feeds were genuinely empty. No synthetic pushed checkpoint was injected, and no fresh post-rollout native pushed event is claimed here. Published ingestion still follows the existing sentinel path.
- Not measured: sustained scale, long-duration CPU/memory behavior or leak-proof redaction. The screenshots/CI/smoke exercise do not establish those claims.
Deployment/recovery ledger · operator guide
Acceptance after an explicit upstream decision
- Code activity is the single successor to the Matrix code view, not another adjacent tab/effect. Migrate navigation, canonical display links, saved display configurations, relevant settings, documentation and streamer references in the same cutover; remove the obsolete view/renderers and dead styles/settings instead of keeping permanent compatibility aliases.
- An eligible identified-Hive PR head reaches the reader through the existing authorized patch-observation path, with a real PR link and visible source/freshness. No new head is invented to keep the display busy.
- Real unified diffs preserve complete admitted add/remove regions, indentation, blanks and repeated lines. Pagination, deduplication and bounded eviction never turn a region into an apparently complete fragment.
- Secret-shaped content on either side drops its whole changed region; denied paths and private/unknown repositories remain absent. Text is rendered as text, never HTML. Revocation/disablement clears retained server and browser code.
- Anonymous and forged-role requests cannot read content; authorized responses remain
no-store. Display/kiosk availability and hub routing do not grant repository/code access. - The actual toolbar entry, pause/resume, manual inspection, quiet hold, explicit replay, narrow-screen wrapping, hidden-tab pause and reduced-motion behavior are exercised on the native surface.
- Only if workspace capture is separately approved: exercise a real post-start edit in an eligible managed workspace and isolated-UID temporary checkout; reject an unregistered/shared owner, ownership/origin changes, symlink replacement and failed public-visibility proof. Configured Git helper/filter traps must not execute during inspection.
- Upstream tests cover consumer-visible data, boundary and transition behavior; docs/changelog identify source semantics and activation status. Measure busy-feed/workspace CPU and memory before making performance claims or broadening defaults.
Alternatives considered
- Retain the existing Matrix code view: rejected as the product direction of this proposal; decorative presence does not provide readable changes or distinguish replay from new work.
- Published diff reader only: the same Code activity replacement with only the published source. It does not require reversing the existing no-pre-push decision and remains an explicit acceptable upstream direction if maintainers keep that boundary.
- Terminal/pane streaming: rejected here; noisier, much more sensitive, and unnecessary for readable code changes.
- Automatic endless replay: looks busy but can misrepresent freshness. Prefer quiet hold and explicit replay.
- Full editor/review UI or hub aggregation: separate products/authorization work; neither is a dependency for this spoke reader.
Scope, compatibility and decisions for maintainers
- Target: current v6 dashboard/display infrastructure; upstream maintainers choose the target branch. Do not merge the entire Tuna fork or its SDLC/deployment changes.
- Operator impact: Code activity supersedes the Matrix code view; the ordinary tracker stays unchanged. Perform one clean UI/configuration-reference/documentation cutover, not a long-lived pair of Matrix and Code activity views. No automatic enablement, permission broadening, GitHub App changes or Twitch activation.
- Contributor/agent impact: keep this issue held; do not create implementation children or treat the fork deployment as approval. If accepted, presentation and workspace collection can be reviewed in separate focused PRs.
Decisions requested:
- Accept Code activity as the replacement for the Matrix code view, including readable whole diff paragraphs, removals, honest freshness and opt-in replay, with the clean cutover described above?
- Explicitly reconsider the prior no-pre-push decision for the separately default-off, public-only workspace source described here, or retain published-only scope upstream?
This proposal requests discussion and upstream review, not immediate autonomous implementation or runtime activation.
Activity
[-]📝 RFC: Passive Code activity reader — readable diffs and separately opted-in workspace snapshots[/-][+]📝 RFC: Supersede the Matrix code view with a passive Code activity reader[/+]hivecommons-hive commentedon Nov 3, 2026
Parking for a maintainer ruling (
stage/045-needs-decision). Risk: security posture / public-facing behaviour.This RFC is self-described as a "held proposal for a new maintainer decision, not accepted upstream work", and two of its parts are not engineering choices the hive may make on its own:
dashboard.matrix.workspacespre-push working-tree capture — the maintainer decision on 📝 RFC: Activity Monitor Matrix mode — ambient code rain of the lines hive is pushing #15862 explicitly restricted Matrix to pushed lines only and excluded working trees; the RFC itself says this part is "separately decision-gated" and needs explicit upstream security review (unpublished and removed text can expose secrets).Please reply with one of:
dashboard.matrix.workspacespre-push collector is in scope (reopening the 📝 RFC: Activity Monitor Matrix mode — ambient code rain of the lines hive is pushing #15862 pushed-only boundary). The hive will decompose it into child issues (reader, published-checkpoint source, workspace collector, cutover/retirement) and implement them in order.Until a ruling lands, no implementation work is started on this issue.
🐝 Hive Agent:
scanner| Instance:hosted-available-oke-11-placeholder-r05x| SHA:unknown— hive: agent=scanner backend=copilot model=claude-fable-5.1 copilot=1.0.88
hivecommons-hive commentedon Nov 3, 2026
What to reply
/hive approve: go with the recommendation/hive decision <your instructions>: go ahead, following your instructions/hive help: show these againIf what this issue waited on has been done (a merged fix, or an action taken outside this repository), a maintainer can reply
/fixedto close it as completed; Hive clears its park labels.Only a maintainer with write access can un-park; everything else is ignored. Full command reference: https://github.com/hivecommons/hive/blob/v5/src/docs/maintainer-commands.md.
hivecommons-hive commentedon Nov 3, 2026
Un-parked by @clubanderson. Decision: B — Accept the published-checkpoint reader as the successor to the Matrix code view (pushed lines only; the #15862 boundary is unchanged). The workspace / pre-push collector stays out of scope and needs its own future decision. Decompose into child issues (reader, published-checkpoint source, cutover and retirement of the Matrix entry point) and implement them in order.
stage/045-needs-decisionis cleared when present andapproved-directionis applied; anyholdlabel is left exactly as it was.Recorded from the hive dashboard.
10 remaining items
hivecommons-hive commentedon Nov 4, 2026
Scanner verification after #16492 (part 1/3) merged: the RFC is not yet resolved. Part 2/3 (#16476) is open as PR #16513 and part 3/3 (#16477, the cutover) is open as PR #16514 — both carry the remaining work and are awaiting review/maintainer decision, so no new PR is needed. Labelled
hive/verified-open; this issue closes with #16514.🐝 Hive Agent:
scanner| Instance:hosted-available-oke-11-placeholder-r05x| SHA:unknown— hive: agent=scanner backend=copilot model=claude-fable-5.1 copilot=1.0.88
hivecommons-hive commentedon Nov 4, 2026
PR #16609 covers this issue: #16609
The PR body says this is partial/non-closing work (
Refs/Part ofor leave-open wording), so Hive will not add a closing keyword. GitHub will not show its issue-list PR icon without a closing keyword; the stage comment is the link.feat(dashboard): replace Matrix presentation with Code activity (#16609)
hivecommons-hive commentedon Nov 4, 2026
All children delivered: #16475 → PR #16492, #16476 → PR #16513, #16477 → PR #16609.
Every tracked child of this issue is closed, so the hive is closing it as completed. Reopen it if something it asked for is still missing.
github-actions commentedon Nov 4, 2026
@hanthor this issue was closed by @hivecommons-hive[bot] as completed.
If this was closed by a merged PR, the fix only takes effect once it ships in a tagged release and your deployment updates to it — check your running version against the fix before concluding the fix failed.
If you are still seeing the problem, comment
/reopenand it will be reopened for you — you do not need write access. Please add what you are still observing (running version, logs, steps) so it is not closed the same way again.