Repository navigation
Home
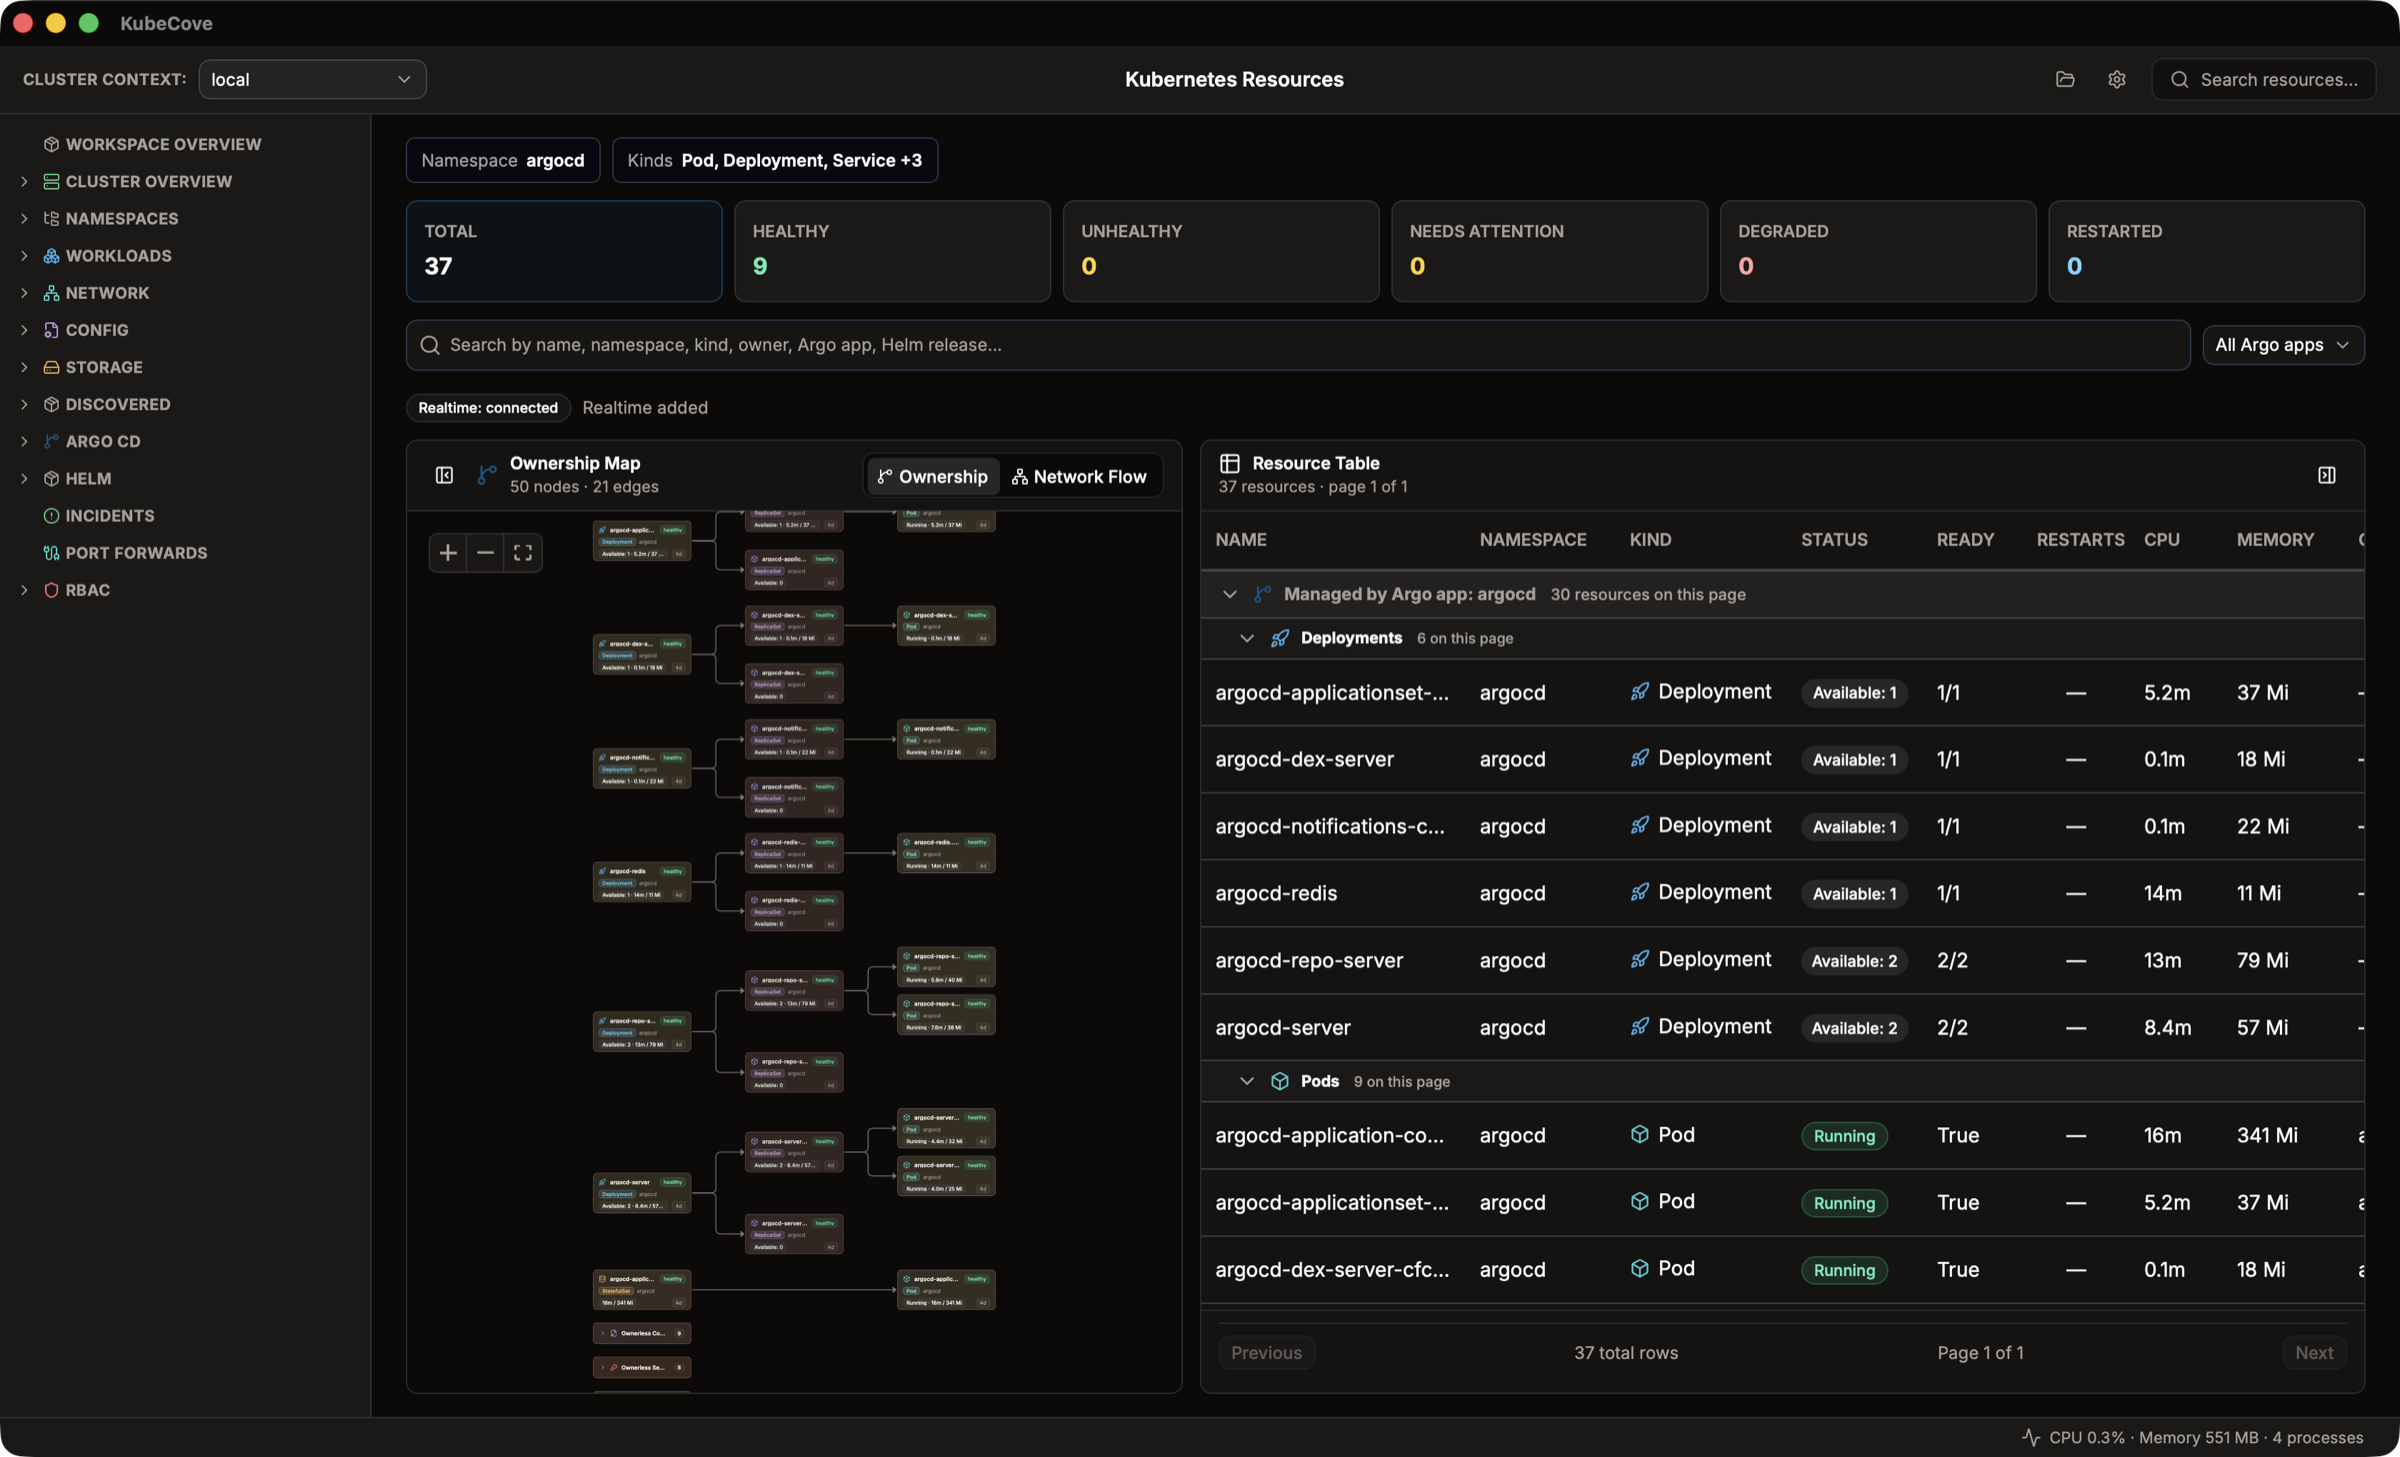
KubeCove is a fast, local Kubernetes desktop GUI for cluster inspection and troubleshooting. It gives Kubernetes-aware operators and application developers a visual resource browser for context, namespace, application ownership, resource state, events, logs, metrics, YAML, topology, GitOps, Helm, and RBAC before taking action.
Kubernetes credentials remain on the Rust side of the desktop boundary. KubeCove does not deploy cluster agents, expose raw kubeconfig contents to the frontend, or provide arbitrary shell execution. Operations are narrow, typed, target-scoped, and explicitly confirmed.
- Download latest installer. Installers are beta builds; OS trust prompts may require approval.
- To keep cluster credentials and connectivity on a remote operations host or an operator-deployed Kubernetes container, follow Run KubeCove on a remote host. The server requires sign-in, and each client gets its own session.
- Make a readable kubeconfig context available through
$KUBECONFIGor your default kubeconfig location. - Create a workspace. Choose a context, then narrow namespaces and resource kinds when useful.
- Open a resource. Inspect details, events, logs, metrics, YAML, ownership, and related GitOps or Helm metadata before using a guarded action.
Inspection is default. Guarded workflows include Pod and selector-backed Service port forwarding, exact-Pod exec, selected-resource YAML apply, reviewed resource actions (scale, pause, restart, rollback, container and metadata edits, delete), and reviewed Argo CD refresh, sync and rollback operations.
YAML apply is limited to selected resources, validates identity, dry-runs before final confirmation, and blocks v1 Secret apply. Argo CD operations use the reviewed transport, while connected inspection can visibly fall back to a complete Kubernetes view when a required connected read fails. Flux remains inspection-only.
- Install and update KubeCove
- Create a workspace and choose scope
- Use the workspace overview
- Browse Kubernetes resources
- Inspect resource details
- Investigate incidents
- Inspect Argo CD and Flux
- Review Helm reconciliation
- Review RBAC and permissions
- Scale, restart, or delete a supported resource
- Edit and apply selected-resource YAML
- Start a guarded Pod exec session
- Start and manage a port forward