




┌──(talha㉿github)-[~/profile]
└─$ whoami
Talha Imran

└─$ cat focus.txt
Cybersecurity • Offensive Security • Penetration Testing • Red Teaming

└─$ cat identity.txt
GitHub:   Talha-imran910
LinkedIn: Talha Imran
Focus:    Cybersecurity / Security Engineering

└─$ cat mindset.txt
Understand the system. Test the system. Secure the system.
Cybersecurity-focused developer and security learner working across penetration testing, offensive security, web security, networking, Linux, Active Directory, cloud security, and security tooling.
I learn by building labs, testing systems in authorized environments, documenting findings, and turning ideas into practical tools.
Security is not about knowing every tool. It's about understanding what the system is doing.
#!/usr/bin/env bash

MISSION="Become exceptionally good at offensive security"

FOCUS=(
  "Penetration Testing"
  "Red Teaming"
  "Web Application Security"
  "Active Directory"
  "Network Security"
  "Linux"
  "Cloud Security"
  "Security Automation"
)

for target in "${FOCUS[@]}"; do
    echo "[+] Learning: $target"
doneNmap · Burp Suite · Wireshark · Metasploit · Gobuster · ffuf · BloodHound · Impacket · NetExec · Responder · Hashcat · John the Ripper · SQLMap · Nikto
Kali Linux · Linux · Windows · Active Directory · VMware · Docker · GitHub Actions
Python · Bash · PowerShell · JavaScript · HTML/CSS · SQL · Git
Python-based reconnaissance tooling focused on automating repeatable information-gathering and enumeration workflows.
Focus: reconnaissance · automation · enumeration · security tooling
A continuously evolving lab for practicing penetration-testing workflows, Linux/Windows enumeration, privilege escalation, Active Directory, and post-exploitation concepts.
Focus: penetration testing · Linux · Windows · Active Directory · privilege escalation
Hands-on security engineering around endpoint monitoring, SIEM/EDR concepts, Sysmon telemetry, file-integrity monitoring, threat intelligence, and incident response.
Focus: Wazuh · Sysmon · SIEM · EDR · threat detection · incident response
More projects, write-ups, experiments, and research will be added as they are published.
                         ┌─────────────────────┐
                         │     ATTACK BOX       │
                         │     Kali Linux       │
                         └──────────┬──────────┘
                                    │
                         Recon / Enumeration
                                    │
                                    ▼
              ┌─────────────────────────────────────┐
              │          CONTROLLED LAB              │
              │                                     │
              │  Windows • Linux • Active Directory │
              │  Web Apps • Network Services        │
              │  Detection / Monitoring             │
              └─────────────────────────────────────┘
                                    │
                                    ▼
                         ┌─────────────────────┐
                         │  DOCUMENT / REPORT  │
                         │  Learn → Build →    │
                         │  Break → Fix        │
                         └─────────────────────┘
My security work is centered around controlled labs and authorized environments. The objective is to understand attack paths deeply enough to reproduce, explain, detect, and mitigate them.
RECON
  ↓
ENUMERATION
  ↓
ATTACK SURFACE MAPPING
  ↓
INITIAL ACCESS
  ↓
PRIVILEGE ESCALATION
  ↓
LATERAL MOVEMENT
  ↓
POST-EXPLOITATION
  ↓
EVIDENCE / IMPACT
  ↓
REPORTING
  ↓
REMEDIATION
I care about why an attack works, not just which command works.
| Area | Topics |
|---|---|
| Offensive Security | Enumeration, exploitation, privilege escalation, post-exploitation |
| Web Security | Authentication, authorization, injection, SSRF, XSS, file handling |
| Active Directory | Kerberos, LDAP, BloodHound, delegation, ACLs, lateral movement |
| Network Security | TCP/IP, subnetting, DNS, DHCP, ARP, scanning, traffic analysis |
| Linux | Permissions, SUID, capabilities, cron, PATH abuse, enumeration |
| Windows | PowerShell, services, tokens, registry, Windows internals |
| Cloud Security | IAM, misconfiguration, identity, attack surface |
| Security Engineering | SIEM, EDR, telemetry, detection, incident response |
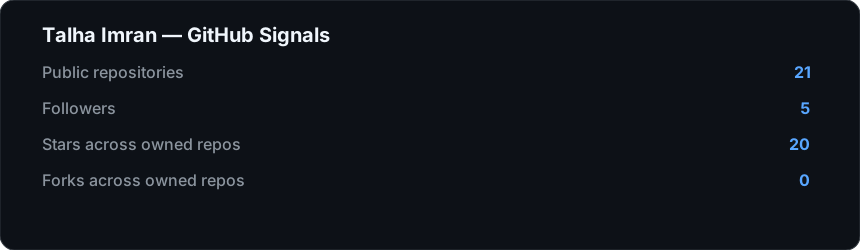
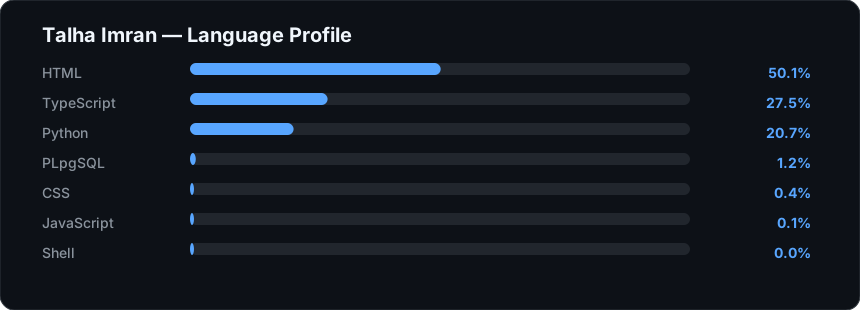


The two main cards above are generated by this repository's own GitHub Action and published to the output branch. That removes the fragile third-party statistics endpoint that was previously responsible for intermittent image failures.
┌─────────────────────────────────────────────────────────────────────┐
│ TALHA IMRAN :: GITHUB ACTIVITY                                      │
├─────────────────────────────────────────────────────────────────────┤
│ [LIVE] PROFILE       → github.com/Talha-imran910                   │
│ [LIVE] CONTRIBUTIONS → github.com/Talha-imran910                   │
│ [LIVE] REPOSITORIES  → github.com/Talha-imran910?tab=repositories   │
│ [LIVE] ACTIVITY      → github.com/Talha-imran910?tab=activity       │
└─────────────────────────────────────────────────────────────────────┘
No fragile activity-graph image is used here. GitHub itself remains the source of truth for activity and contributions.


I deliberately removed the old trophy generator. Your actual GitHub achievements are displayed by GitHub itself, so the profile will never claim an achievement that you have not earned.
Generated automatically from Talha Imran's contribution graph by .github/workflows/snake.yml and published to the output branch.
Scope:
  Authorized security research
  CTFs and educational labs
  Defensive security experimentation
  Open-source security tooling

Principles:
  Learn responsibly.
  Test with authorization.
  Document everything.
  Share knowledge without enabling abuse.

If you're interested in cybersecurity, penetration testing, red teaming, security engineering, or open-source security projects, explore the repositories and connect through the profiles above.
Building security tools.
Breaking things in labs.
Studying how systems fail.
Learning how to defend them.

One shell at a time.