Repository navigation
feat(mssql): add explicit login impersonation for linked-server execution - #1443
Open
BrunoRochaDev wants to merge 3 commits into
Open
BrunoRochaDev wants to merge 3 commits into
BrunoRochaDev wants to merge 3 commits into
Conversation


BrunoRochaDev
requested review from
Marshall-Hallenbeck,
NeffIsBack,
mpgn and
zblurx
as code owners
September 23, 2026 11:20

Member
|
Thanks for the PR! Looks cool :) Related: #1067 |

This file contains hidden or bidirectional Unicode text that may be interpreted or compiled differently than what appears below. To review, open the file in an editor that reveals hidden Unicode characters.
Learn more about bidirectional Unicode characters
Sign up for free
to join this conversation on GitHub.
Already have an account?
Sign in to comment


Add this suggestion to a batch that can be applied as a single commit.This suggestion is invalid because no changes were made to the code.Suggestions cannot be applied while the pull request is closed.Suggestions cannot be applied while viewing a subset of changes.Only one suggestion per line can be applied in a batch.Add this suggestion to a batch that can be applied as a single commit.Applying suggestions on deleted lines is not supported.You must change the existing code in this line in order to create a valid suggestion.Outdated suggestions cannot be applied.This suggestion has been applied or marked resolved.Suggestions cannot be applied from pending reviews.Suggestions cannot be applied on multi-line comments.Suggestions cannot be applied while the pull request is queued to merge.Suggestion cannot be applied right now. Please check back later.
Description
This change adds explicit MSSQL login impersonation support to the
exec_on_linkmodule.While using NetExec in an MSSQL linked-server lab, I found that
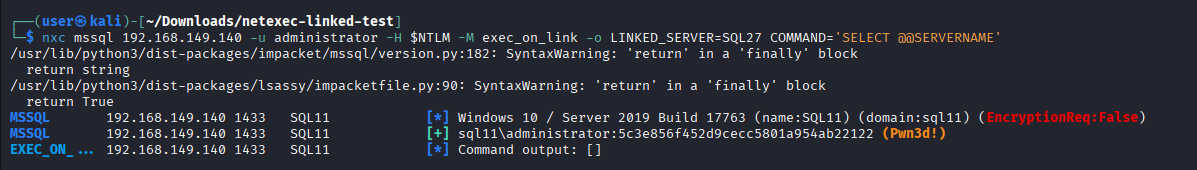
exec_on_linkcould return an empty result when the authenticated login did not have a linked-server login mapping.For example, I attempted to execute a query through a linked server:
The module didn't return any errors, but also there was no command output. It just silently failed.
Running the query manually showed the actual MSSQL error:
The
enum_linksmodule showed that the server had a mapping for local loginwebapp11, rather than the authenticated administrator login.Manually impersonating that login allowed execution through the linked server:
To address this, I created this PR that adds an explicit
AS_LOGINoption toexec_on_link:The implementation uses statement-scoped
AS LOGINsyntax:This keeps impersonation explicit and scoped to the linked-server command, without leaking to further queries or anything of the sort.
The module now also:
AS_LOGIN=<login>retry hints without selecting one automatically.--queryoutput instead of displaying raw Python dictionaries.AS_LOGIN, but prevents quotes in commands/login names and closing brackets in linked-server names from breaking the dynamically constructed wrapper query.I manually tested this contribution on some of the OSEP challenge labs, and it works fine.
AI assistance disclosure
I discovered this limitation organically while using NetExec in my OSEP studies. I investigated the existing code, repository documentation, git history, and available discussions to confirm that this functionality was not already implemented or being contributed in an existing PR.
I then used Codex GPT-5.6-Terra as an implementation assistant. It helped investigate the relevant code paths, propose the implementation approach, and generate code changes. I reviewed the changes and tested them manually in labs.
I wrote this PR description myself, although I used LLMs for paraphrasing in some places.
Related discussion: Reworking part of the MSSQL protocol
Type of change
Insert an "x" inside the brackets for relevant items (do not delete options)
Setup guide for the review
Testing was performed from a Kali Linux VM against an MSSQL linked-server lab (from the OSEP challenge labs).
The original behavior can be reproduced by authenticating as a login without a mapping and running:
nxc mssql ... -M exec_on_link -o LINKED_SERVER=<SERVER-NAME> COMMAND='SELECT @@SERVERNAME'Before this change, the module displayed an empty result even though SQL Server reported a missing login mapping (as shown in the following screenshots).
The new behavior was tested with:
nxc mssql ... -M exec_on_link -o LINKED_SERVER=<SERVER_NAME> AS_LOGIN=<LOGIN> COMMAND='SELECT @SERVERNAME'This successfully executed the query through the linked server and returned formatted output.
Screenshots (if appropriate):
Before (no query execution):
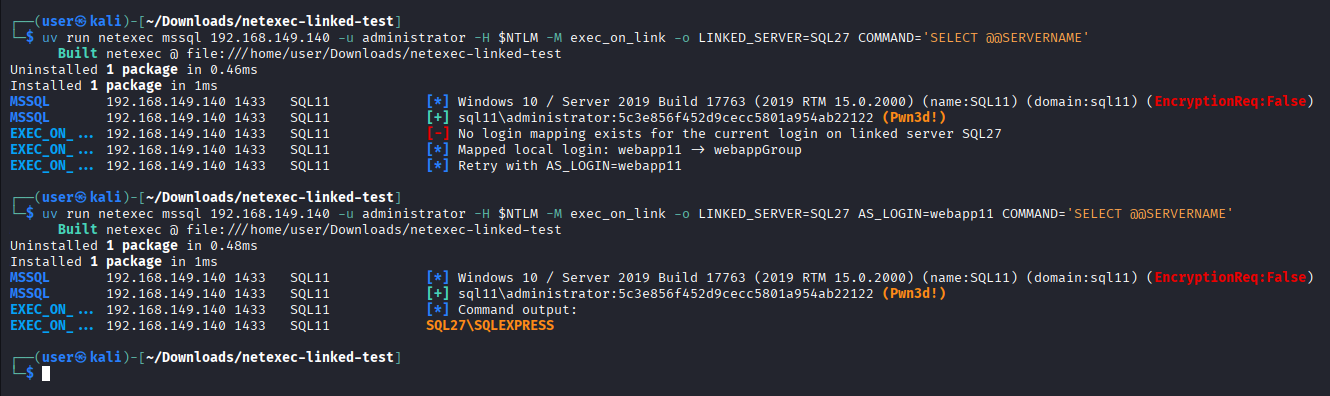
After (explicit errors, guides the user in the right direction, query execution):
Checklist:
Insert an "x" inside the brackets for completed and relevant items (do not delete options)
poetry run ruff check ., use--fixto automatically fix what it can)tests/e2e_commands.txtfile if necessary (new modules or features are required to be added to the e2e tests)